Cybersecurity Talent for a Threat Landscape That Keeps Changing.
Security Is No Longer a Technology Function Sitting Beside the Business.
As organizations become more digital, the boundary between technology and security becomes harder to separate. Applications are business infrastructure. Cloud environments are business infrastructure. Identity systems are business infrastructure.
Data is business infrastructure. AI is becoming business infrastructure.
And every new layer creates another security consideration. That changes the talent requirement. Cybersecurity teams today need people who can prevent attacks, detect threats, secure applications and infrastructure, manage identities, respond to incidents and help organizations understand and manage risk.
TalentiFi-X helps organizations identify cybersecurity professionals across this increasingly interconnected landscape.
Cybersecurity Has Become an Ecosystem.
The traditional picture of cybersecurity often centered around network security, antivirus and security operations. Those remain important.
But modern security teams can span:
- Identity
- Cloud
- Applications
- Data
- Infrastructure
- AI
- People
- Governance
That means cybersecurity hiring is becoming increasingly specialized. A company looking for a cloud security engineer is solving a different problem from a company looking for a penetration tester. A SOC may need detection and response expertise. A SaaS company may need application security.
A regulated enterprise may need stronger governance and risk capabilities. A growing organization may need its first security leader. The common requirement is security. The capability is different.
The Cybersecurity Talent Spectrum.
Security Engineering
Professionals who design and implement technical controls to protect systems, applications, infrastructure and data.
Cloud Security
Security professionals focused on protecting cloud environments, identities, workloads, infrastructure and configurations across platforms such as AWS, Azure and Google Cloud.
Application & Product Security
Security professionals working alongside engineering and product teams to identify vulnerabilities and build security into the software development lifecycle.
Security Operations
Professionals monitoring environments, investigating alerts, detecting threats and responding to security events.
Identity & Access Management
Specialists responsible for authentication, authorization, privileged access and identity lifecycle management.
Threat Intelligence
Professionals who analyze threat actors, vulnerabilities, attack patterns and intelligence to help organizations anticipate and respond to threats.
Incident Response
Specialists who investigate and manage security incidents, helping organizations contain threats and recover from them.
DevSecOps
Professionals integrating security into software development, infrastructure and deployment processes.
Security Architecture
Senior professionals designing security frameworks and architectures across complex technology environments.
Governance, Risk & Compliance
Professionals connecting security controls with organizational risk, regulatory requirements, policies and governance.
AI Security
An increasingly important area covering security considerations around AI models, applications, data, infrastructure and AI-enabled systems.
Roles Across the Cybersecurity Landscape.
Depending on the requirement, organizations may hire for roles such as:
- Cybersecurity Engineer
- Security Engineer
- Information Security Engineer
- Cloud Security Engineer
- Application Security Engineer
- Product Security Engineer
- Network Security Engineer
- Security Architect
- Cloud Security Architect
- DevSecOps Engineer
- Security Operations Analyst
- SOC Analyst
- SOC Engineer
- Detection Engineer
- Threat Detection Engineer
- Threat Intelligence Analyst
- Incident Response Specialist
- Digital Forensics Specialist
- Vulnerability Management Specialist
- Penetration Tester
- Ethical Hacker
- IAM Engineer
- Identity Security Specialist
- Privileged Access Management Specialist
- Security Automation Engineer
- GRC Analyst
- Cyber Risk Specialist
- Security Compliance Specialist
- Security Program Manager
- Security Engineering Manager
- Head of Cybersecurity
- Head of Information Security
- CISO
The title can tell you where someone sits. It does not necessarily tell you what security problem they can solve.
Don't Hire for the Certification. Hire for the Capability.
Cybersecurity is one of the areas where credentials can be particularly visible. CISSP. CISM. CEH. OSCP. Cloud certifications. Security vendor certifications. They can all provide useful signals. But a certification does not automatically tell you how someone behaves when a real security problem appears at 2 a.m.
- Can they investigate?
- Can they prioritize?
- Can they distinguish signal from noise?
- Can they communicate risk clearly?
- Can they work with engineering teams?
- Can they make decisions with incomplete information?
- Can they take ownership?
Certification can demonstrate knowledge. Experience reveals judgment.
That distinction matters when hiring for security-critical roles.
Security and Engineering Are Becoming More Connected.
Security can no longer be treated as something that happens after software has been built.
Modern security increasingly needs to work alongside:
- Software engineering
- Cloud engineering
- Platform engineering
- Data engineering
- Product management
- Infrastructure
- AI teams
This is one reason DevSecOps has become an important part of modern technology organizations. Security controls need to exist within the workflow. Not simply at the end of it. The same principle applies to application security. The later a security problem is discovered, the more expensive and disruptive it can become to fix.
That means organizations increasingly need security professionals who can communicate with engineers and understand how products are actually built.
Cloud Has Changed the Security Job.
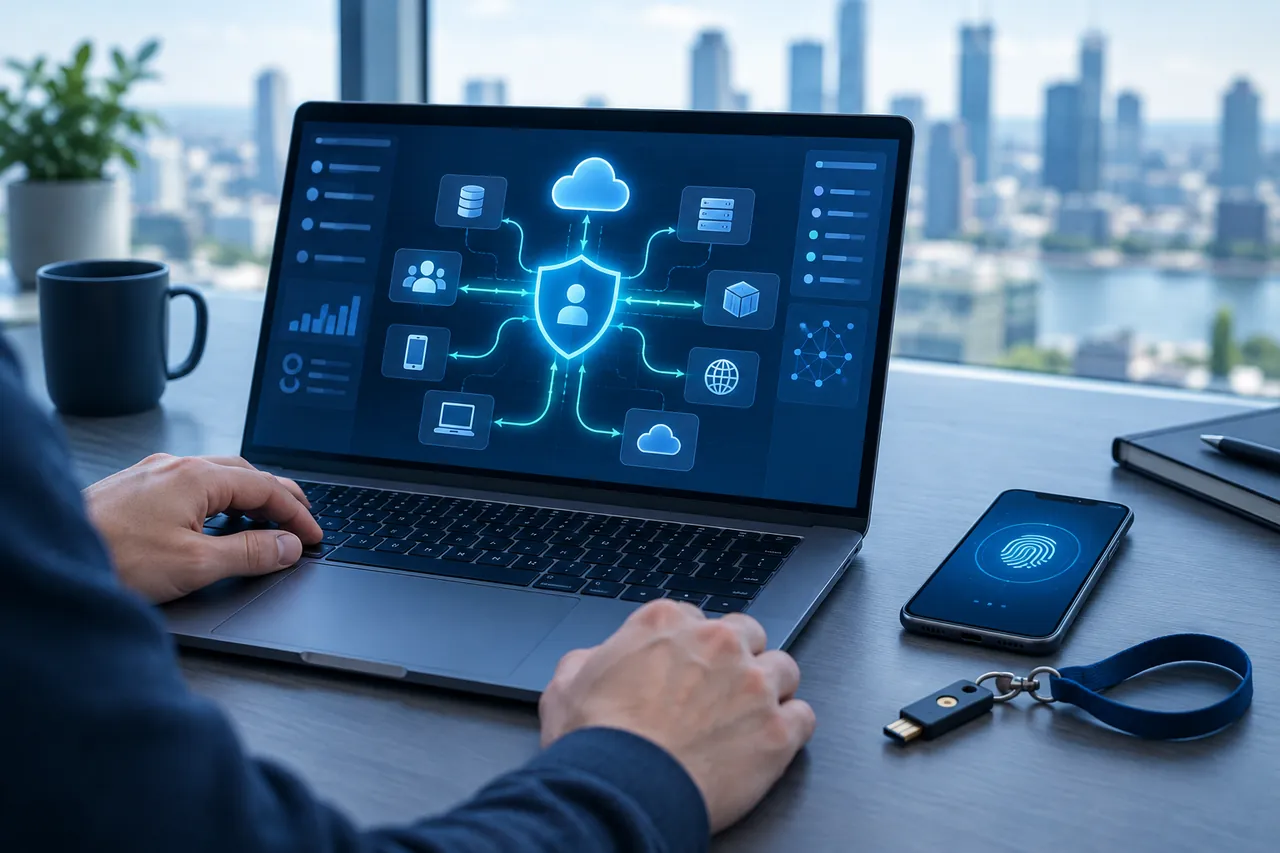
Traditional security models assumed that infrastructure existed inside relatively defined boundaries. Cloud environments changed that.
Infrastructure can now be:
- distributed
- dynamic
- programmable
- ephemeral
- multi-cloud
- hybrid
- accessed from anywhere
Identity can become the new perimeter. Infrastructure can be created through code. Applications can scale automatically. That means cloud security professionals increasingly need to understand both security and cloud engineering.
The strongest candidates may therefore sit at the intersection of:
- Cloud
- Identity
- Infrastructure
- Security
- Automation
AI Is Creating a New Security Layer.
Artificial intelligence introduces new opportunities. It also introduces new security questions.
Organizations deploying AI may need to consider:
- Data exposure
- Model access
- Identity and permissions
- Prompt injection
- Model misuse
- Application vulnerabilities
- Supply-chain risks
- AI infrastructure security
- Sensitive information handling
- Monitoring and governance
This is creating demand for professionals who understand the intersection between AI and cybersecurity. The exact role may not always have a standardized title. That makes capability-based hiring even more important.
What Good Cybersecurity Talent Looks Like.
Technical expertise is essential. But security is also a judgment profession.
Technical Depth
Does the candidate genuinely understand the systems they are securing?
Threat Thinking
Can they think about how a system could be attacked rather than simply how it is supposed to work?
Investigation
Can they follow evidence and determine what actually happened?
Risk Judgment
Can they distinguish a theoretical vulnerability from a material business risk?
Communication
Can they explain a technical security issue clearly to engineering teams and business leadership?
Business Understanding
Do they understand the consequences of security decisions?
Adaptability
Can they learn as attack methods, technologies and environments change?
Ownership
Will they take responsibility when a security problem becomes real?
The Security Professional Needs to Understand the Business.
There is a subtle difference between "This system has a vulnerability." and "This vulnerability creates a meaningful risk to this business because..." The second statement is much more useful to a leadership team.
Security professionals increasingly need to communicate in terms of:
- Business impact
- Customer impact
- Operational risk
- Financial exposure
- Regulatory consequences
- Reputation
- Prioritization
This does not make technical depth less important. It makes context more important.
The best security decisions connect technical reality to business consequence.
Cybersecurity Hiring Across the USA and India.
Cybersecurity talent is important across both established technology markets and rapidly expanding digital ecosystems. US organizations may be building security teams around cloud, application security, identity, AI and enterprise risk.
Read moreShow less
Indian organizations may be expanding security operations, cloud security, engineering security and global technology capabilities. Global Capability Centers can also create complex security requirements because teams may operate technology, infrastructure and security functions supporting businesses across multiple markets.
This creates demand for professionals who can work across:
- Technology
- Security
- Geography
- Regulation
- Business Context
TalentiFi-X supports cybersecurity hiring requirements across the United States and India, depending on the organization's role, capability and engagement requirements.
When Cybersecurity Hiring Becomes Difficult.
Cybersecurity hiring can become particularly challenging when:
- The role combines multiple security disciplines.
- The organization needs both security and engineering experience.
- A role requires cloud and cybersecurity expertise.
- Application security must work closely with product engineering.
- Security teams need specialized detection or incident response capabilities.
- The organization is building a security function from scratch.
- Internal hiring teams are struggling to evaluate technical security talent.
- The role requires senior security leadership.
- A GCC is building or scaling cybersecurity capabilities.
- The organization needs talent with emerging AI security expertise.
In many cases, the problem is not that there are no cybersecurity professionals. It is that the right combination of capabilities is difficult to identify.
A Better Way to Think About Cybersecurity Hiring.
Before defining a security role, ask:
What are we protecting?
Applications? Data? Infrastructure? Identities? Customers? Intellectual property?
Where does the risk exist?
Cloud? Endpoint? Application layer? Identity? Network? AI systems?
What happens if something goes wrong?
The answer helps determine how much technical and business context the role requires.
What capability is missing?
Security engineering? Detection? Architecture? Governance? Leadership?
Where does the role sit?
Inside security? Engineering? Product? Infrastructure? Risk?
These questions can produce a much more useful hiring brief than simply writing: "Looking for a cybersecurity professional."
How TalentiFi-X Approaches Cybersecurity Hiring.
Cybersecurity hiring starts with understanding the security problem. That means looking at the environment, the role, the technical requirements, the business context and the level of responsibility involved. Technology can assist in identifying relevant professionals.
Human judgment remains essential in understanding whether their experience actually translates to the environment and risk profile of the organization. Because cybersecurity is not simply about finding someone who knows the tools.
It is about finding someone you can trust with the problem.
The Future of Cybersecurity Talent.
Cybersecurity is becoming increasingly interconnected with the rest of technology.
The future security professional may need to understand:
- Cloud
- Software
- Identity
- Data
- AI
- Automation
- Risk
That does not mean every security professional needs to become an expert in everything. It means organizations need to become more precise about which combination of capabilities each role actually requires. That is where modern cybersecurity hiring needs to evolve. Not toward more resumes. Toward better understanding.
Keep exploring.
Related insights
- ArticleHow to Choose an IT Staffing Agency in the USA in 2026Most IT staffing agencies promise the same things. These 10 questions help you find the one that can actually deliver the right people for your contract, contract-to-hire or direct hire technology roles.Read more
- ArticleToo Many Job Applications, Not Enough Qualified Candidates: What's Broken in Hiring?Some companies receive hundreds of applications for a single role and still cannot find candidates who meet their requirements. Here is why application volume is not candidate quality, and what employers can do about it.Read more
- ArticleContract Staffing in India: A Complete Guide for Employers in 2026Contract staffing gives employers in India a way to bring in specialized capability for as long as the business needs it. This guide covers how it works, what it costs, compliance and how to choose a partner.Read more
Cybersecurity staffing is the process of identifying and hiring professionals across cybersecurity, information security, security engineering, security operations, cloud security, application security, identity and related functions.
Roles can include security engineers, cloud security engineers, application security engineers, SOC analysts, detection engineers, incident response specialists, penetration testers, IAM professionals, DevSecOps engineers, security architects, GRC specialists and cybersecurity leadership.
The specific requirements depend on the role, but relevant capabilities can include security engineering, threat detection, incident response, cloud security, application security, identity management, risk management, security architecture and communication.
Certifications can provide useful evidence of knowledge, but they should generally be considered alongside practical experience, problem-solving ability, technical depth, judgment and role-specific capability.
The terms are often used interchangeably, although organizations may use them differently. Cybersecurity generally focuses heavily on protecting digital systems, networks, applications and data from cyber threats, while information security can encompass the broader protection of information and related risks.
DevSecOps integrates security practices into software development, infrastructure and deployment processes rather than treating security as a separate final-stage activity.
As organizations move infrastructure and applications into cloud and hybrid environments, security teams need to understand dynamic infrastructure, identity, access, configuration, workloads and cloud-specific risks.
AI is creating new security considerations around AI applications, models, data, infrastructure and usage. This can create demand for professionals with overlapping AI, security, engineering and governance capabilities.
TalentiFi-X supports technology hiring requirements in the United States, including cybersecurity roles, depending on the specific requirement and engagement model.
Yes. TalentiFi-X supports technology hiring requirements in India across cybersecurity, information security and related technology capabilities.
TalentiFi-X can support contract cybersecurity hiring where the role and engagement model align with its staffing services.
Security Starts With People Who Understand the Risk.
Technology can identify signals. Tools can detect threats. Automation can accelerate response. But organizations still need people who can understand what matters, make decisions and take responsibility. Build a security team that understands more than the technology.